
Most breaches do not start with a clever exploit. They start with a login that already belongs to someone else. An employee password leaks in a third-party breach, an infostealer strips saved credentials from a personal laptop and the data lands on a breach forum days before anyone notices. For a managed security service provider, that timeline is the problem. Your clients cannot check every underground source themselves and you cannot afford to do it by hand for dozens of client domains.
That is the case for MSSP dark web monitoring: a continuous, automated service that watches criminal sources for your clients exposed credentials, domains and data, then routes findings to the people who can act on them. Done well, it gives your team an early warning layer and gives your clients visible proof that you are working for them between incidents. A dedicated MSSP dark web monitoring platform handles the heavy lifting of collection, matching and alerting, so your analysts spend their time on response instead of searching.
What Is MSSP Dark Web Monitoring?
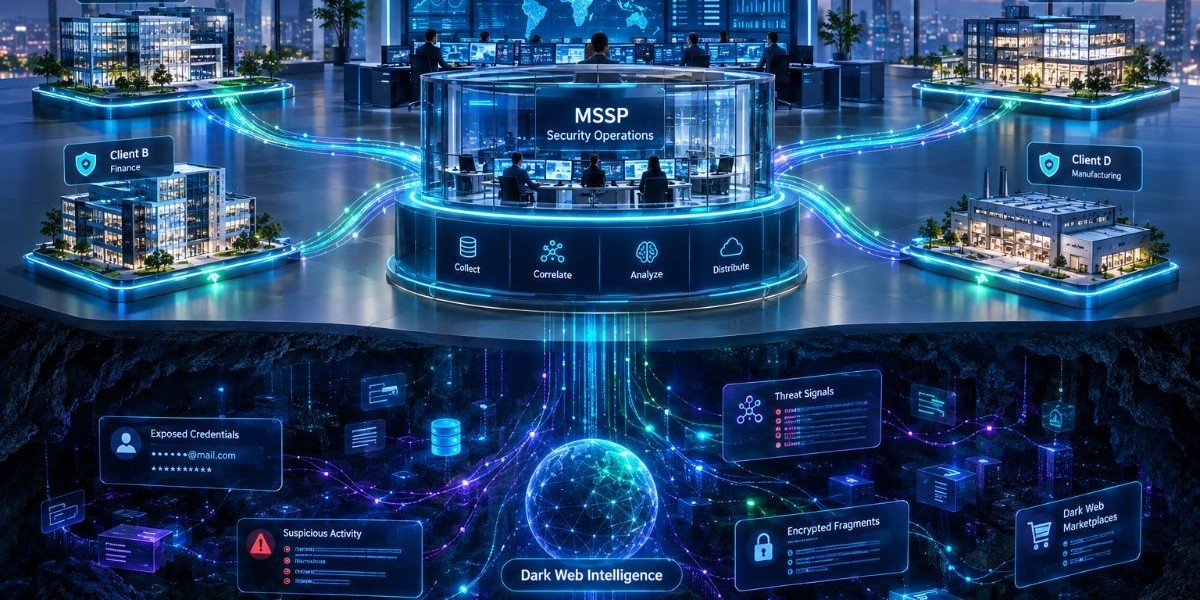
MSSP dark web monitoring is a managed service in which a security provider continuously scans dark web marketplaces, breach forums, paste sites and infostealer log channels for data tied to a client's domains, email addresses and brand. When a match appears, the provider alerts the client, assesses the risk and guides remediation. The MSSP version differs from consumer tools because it must work across many clients at once.
Three points separate it from the consumer identity-protection products most people know:
It monitors at the domain level, so every address at a client company is covered without enrolling each employee one by one.
It is multi-tenant, meaning each client's data stays isolated inside one provider-run environment.
It is delivered as a service, so findings flow into your existing workflows, reports and client conversations.
You will also see this called dark web threat monitoring, dark web exposure monitoring, or dark web threat intelligence for MSSPs. The labels vary. The core job is the same: find exposed client data early and turn it into action.
What It Does and Does Not Cover
Dark web monitoring looks for exposure that has already happened. It finds leaked credentials, stolen session data and mentions of a client's domain in criminal spaces. It does not block an attack in progress and it does not replace endpoint protection, MDR, or email security. Think of it as the layer that tells you a door key has been copied, while your other tools guard the doors.
Coverage is also never total. Many criminal communities are closed, invite-only, or move to new platforms quickly. A credible provider will tell you that plainly. Any vendor claiming to see the entire dark web is overstating what is possible.
How MSSP Dark Web Monitoring Works
Dark web monitoring works in a repeating pipeline: collect data from criminal sources, normalize it, match it against client assets, score the result and deliver an alert. Each stage affects the quality of what your analysts see, which is why two platforms with similar marketing can behave very differently in daily use.
Collection
Platforms gather data from several source types. These include dark web marketplaces, breach forums, paste sites, messaging channels, ransomware leak sites and infostealer logs. Collection may combine automated crawlers, feeds from data partners and human intelligence work. The mix matters, because automated crawling alone tends to miss closed communities.
Normalization
Raw leaked data is messy. A dump may contain mixed formats, duplicate records and inconsistent fields. Normalization cleans it into structured records: email, password or hash, source, date, and any extra context such as a URL or device detail. Without this step, matching is noisy and duplicates flood the alert queue.
Matching
The platform compares normalized records against the domains, emails and keywords registered for each client. Domain-level matching is the practical choice for providers, because it catches every address at the client company, including ones the client forgot existed. This is also where multi-tenant design pays off, since one incoming record can be checked against every client in a single pass.
Scoring and Enrichment
Not every exposure is equal. A plaintext password from a fresh infostealer log deserves urgent attention. A hashed password from a breach several years old usually does not. Good platforms add context such as source type, data freshness and whether the credential appears to be active, then rank findings so analysts start with the riskiest ones.
Alerting and Delivery
Findings reach your team through a dashboard, email, or an integration into a ticketing system, SIEM, or SOAR workflow. The best setups also let you deliver client-facing reports under your own brand. The same principles of tuning and routing apply to any managed monitoring workflow.
Why MSSPs Need Dark Web Monitoring
MSSPs need dark web monitoring because credential-based attacks are one of the most common ways attackers get in and exposed credentials are detectable before they are used. Adding MSSP dark web monitoring to your service stack gives providers an early warning signal, a recurring service line and a tangible way to show value. All three matter in a market where clients constantly ask what they are paying for.
Credentials Are a Primary Attack Path
Industry breach research consistently ranks stolen credentials among the leading causes of breaches. According to Verizon's 2026 Data Breach Investigations Report, stolen credentials were involved in 39 percent of breaches it analyzed. Attackers use leaked logins for credential stuffing, account takeover and initial access, often against accounts that lack strong multi-factor authentication.
Infostealer malware has made this worse. It harvests saved passwords, cookies and session tokens from infected devices and the logs are sold or shared on criminal channels. A stolen session token can bypass a password entirely, which is why credential monitoring alone is no longer enough. Your platform should cover infostealer data, not just old breach dumps.
It Creates a Visible, Recurring Service
Much of what an MSSP does is invisible when it works. Dark web monitoring is different, because a specific finding is easy to explain: here is an employee email, here is where it appeared, here is what we did about it. That makes quarterly reviews and renewals easier, since you can point to real events instead of abstract coverage.
It Supports Prospecting
Exposure data is also a strong conversation starter with prospects. A domain exposure summary shows a company something concrete about its own risk, which is far more persuasive than a generic pitch. Many providers use a light exposure check as the first step in a sales conversation, then convert to a managed service. Platforms that include prospecting tools built for this workflow save you from stitching together separate products.
It Supports Compliance and Insurance Conversations
Clients increasingly face questions from auditors, customers and cyber insurers about how they detect exposed credentials. Documented monitoring and response records give you clear answers. Be careful here: monitoring supports a compliance program, but it does not by itself make a client compliant with any framework. Describe it as evidence of a control, not as certification.
Key Features to Look for in an MSSP Dark Web Monitoring Platform
The right platform is built for providers, not adapted from a single-company product. Look for multi-tenant architecture, role-based access control, white-label delivery, infostealer coverage, domain-level monitoring, alert prioritization and integrations. These features determine whether the service scales across your client base without adding headcount.
Multi-Tenant Architecture
You will manage many clients from one console. Multi-tenant design keeps each client's assets, alerts and reports separate while giving you a single view across all of them. Without it, you end up juggling separate logins or accounts, which breaks down past a handful of clients.
Role-Based Access Control (RBAC)
RBAC controls who sees what. Analysts may need access to every client, account managers only to their own and client users only to their own environment. Granular permissions protect sensitive findings and reduce the risk of one client seeing another's data.
White-Label Delivery
If you resell the service, it should carry your brand. White-label options let you present the dashboard, reports and alerts as your own product, with your name, logo and domain. This keeps the client relationship with you and turns monitoring into part of your own offering rather than a visible third-party tool.
Infostealer Log and Breach Forum Coverage
Ask specifically where the data comes from. Infostealer logs, breach forums, marketplaces, paste sites and ransomware leak sites each show different kinds of exposure. A platform that relies on a single source type will leave gaps. Ask how quickly new data reaches the platform and be wary of vague answers.
Domain-Level Monitoring
Monitoring by domain covers every address in a client organization automatically, including new hires and forgotten mailboxes. Per-email enrollment does not scale and misses exposure on addresses nobody thought to add.
Alert Prioritization and Deduplication
An unfiltered feed of every historical leak will bury your analysts. Look for severity scoring, deduplication of repeat exposures and the ability to separate fresh findings from old ones. Alert fatigue is the most common reason monitoring services get ignored.
Integrations and API Access
Findings are most useful inside the tools your team already works in. Check for API access and connections to ticketing, PSA, SIEM and SOAR platforms, so an alert can become a ticket without manual copying.
Client Reporting
Clients want to see what you found and what you did about it. Look for scheduled, exportable reports you can brand and send, plus a client portal if you want clients to self-serve.
Comparing Approaches to Dark Web Monitoring for MSSPs
Providers generally choose among four routes: manual checks with free tools, building in-house, adopting an enterprise threat intelligence platform, or using a white-label platform designed for MSSPs. Each fits a different stage and budget and the differences show up mostly in scalability and effort.
Approach | Multi-Client Support | Setup Effort | Ongoing Effort | Best Fit |
Manual checks with free tools | None, one lookup at a time | Low | High and repetitive | One-off checks or prospecting |
In-house build | Custom, depends on your engineering | Very high | High, needs dedicated staff | Large providers with intelligence teams |
Enterprise threat intelligence platform | Varies, often built for one organization | Medium to high | Medium | Single large enterprises |
White-label MSSP platform | Built in through multi-tenant design and RBAC | Low to medium | Low, mostly triage and response | Providers reselling to many clients |
The manual route is fine for a quick check but does not scale. Building in-house gives control, but the cost of acquiring and maintaining underground data access is easy to underestimate. Enterprise platforms are powerful, yet many are priced and structured for a single organization rather than a portfolio of clients. A white-label platform usually fits providers best, because it packages the data, the multi-tenant structure and the branding together.
Common Mistakes When Offering Dark Web Monitoring
The most common mistakes are treating monitoring as a report instead of a workflow, ignoring infostealer data, skipping a defined response process and overpromising coverage. Each one weakens the service and can damage client trust. They are all avoidable with some planning before launch.
Sending alerts with no response plan. An alert that says a password leaked is only useful if the client knows what happens next. Define who resets credentials, who checks for suspicious logins and who confirms multi-factor authentication is on.
Relying only on old breach data. Historical dumps show that an address was exposed at some point, but fresh infostealer logs show active compromise. Treat them differently.
Overpromising coverage. Never tell a client you monitor the entire dark web. Explain what sources you cover and what you cannot see.
Ignoring alert volume. Without deduplication and severity scoring, analysts learn to skim and real findings get missed.
Skipping client education. Clients who do not understand what an alert means will either panic or ignore it. A short explainer at onboarding prevents both.
Treating monitoring as a standalone product. It works best alongside MFA enforcement, password hygiene and endpoint protection. Monitoring tells you about the exposure and those controls reduce the damage.
A Practical Evaluation Checklist
Before choosing a platform, run it through a short checklist. The goal is to test how it behaves as a multi-client service, not just how its demo looks.
Does it support multi-tenant management with separate client environments?
Can you set role-based permissions for analysts, account managers and client users?
Can you fully white-label the dashboard, alerts and reports?
Which source types does it cover and does that include infostealer logs?
Does it monitor by domain and how are new addresses picked up?
How does it separate fresh exposures from historical ones?
What integrations and API options exist for your ticketing and SIEM tools?
Can you generate branded client reports without manual formatting?
What is the pricing model and does it scale sensibly as you add clients?
What does onboarding look like for a new client and how long does it take?
Ask for a trial against a real domain and judge the results yourself. Check whether findings are relevant, current and clearly explained.
Interesting Facts About Dark Web Monitoring
These points come from published industry research and public sources. Where exact figures change each year, check the latest edition of the report.
According to Verizon's 2026 Data Breach Investigations Report, stolen credentials were a factor in 39 percent of the breaches it analyzed, which is why credential exposure is a core monitoring target.
Industry breach reports regularly list credential abuse and phishing among the top initial access methods and they publish updated rankings each year.
Infostealer malware collects saved passwords, browser cookies and session tokens and the resulting logs circulate on criminal channels. Security research firms track these logs as a distinct threat category.
Have I Been Pwned, run by security researcher Troy Hunt, catalogs data from publicly known breaches and lets people check if an address appeared in them. It covers known breaches, not continuous underground monitoring.
IBM's annual Cost of a Data Breach Report tracks how long breaches take to identify and contain and it consistently shows that faster detection is tied to lower costs.
The Tor Project has published estimates of the number of active onion service addresses and it notes that they represent a very small share of the overall web. Much criminal activity also happens on invite-only forums and messaging platforms that are harder to observe.
Conclusion
MSSP dark web monitoring gives providers an early view of exposed client credentials and data, turns that view into a visible service and creates a natural bridge to prospecting and renewals. When you evaluate platforms, focus on what your team will actually use every day: multi-tenant structure, RBAC, white-label delivery, infostealer coverage and alerts that are prioritized instead of overwhelming. Test with real domains, be honest with clients about coverage limits and pair monitoring with MFA and password hygiene so alerts lead to action. To see how a white-label option fits a provider model, explore what Mispar offers for MSSPs.
Frequently Asked Questions (FAQs)
What is MSSP dark web monitoring?
MSSP dark web monitoring is a managed service where a security provider continuously watches dark web marketplaces, breach forums, paste sites and infostealer logs for client credentials and data. When exposure is found, the provider alerts the client and guides remediation.
How does dark web monitoring work for managed security service providers?
Platforms collect data from criminal sources, normalize it and match it against each client's registered domains and emails. They then score findings by severity and deliver alerts through a dashboard, email, or integrations with ticketing and SIEM tools.
What features should an MSSP look for in a dark web monitoring platform?
Look for multi-tenant architecture, role-based access control, white-label branding, infostealer log coverage, domain-level monitoring, alert prioritization, API access and branded reporting. These features let you scale across many clients without adding manual work.
Can MSSPs resell dark web monitoring under their own brand?
Yes, if the platform supports white-label delivery. A white-label platform lets you present the dashboard, alerts and reports under your own name, logo and domain, so the service appears as part of your offering.
Is dark web monitoring the same as threat intelligence?
Not exactly. Dark web monitoring focuses on finding exposed client data, such as credentials and domain mentions. Threat intelligence is broader and covers attacker tactics, indicators of compromise and campaign analysis.
Does dark web monitoring stop breaches?
No. Dark web monitoring detects exposure that has already occurred, which lets you act before attackers use the data. It works best alongside multi-factor authentication, password hygiene and endpoint protection.